Setting up and securing your server
First, we’re going to update and upgrade all our applications on our operating system to ensure that our system is up to date. Enter the command below in your terminal.
sudo apt-get update && sudo apt-get upgrade -y
Next, we’re going to install htop: an interactive system-monitor process-viewer, and process-manager. Enter the command below in your terminal.
sudo apt install htop
Once completed, we’re going to create a new user. You will be asked to choose a password for this new user. You can optionally enter full name, room number, etc.; to skip, press Enter every time. Enter the command below in your terminal. Note: testnode should be changed with your personally chosen username.
adduser testnode
Next, we’re going to give this new user sudo privileges. Sudo is an acronym for superuser do, a command that runs an elevated prompt without a need to change your identity. Enter the command below in your terminal. Note: testnode should be changed with your personally chosen username.
adduser testnode sudo
Now we’re going to configure the Secure Shell Protocol (SSH), which is a cryptographic network protocol for operating network services securely over an unsecured network. Enter the command below in your terminal.
sudo nano /etc/ssh/sshd_config
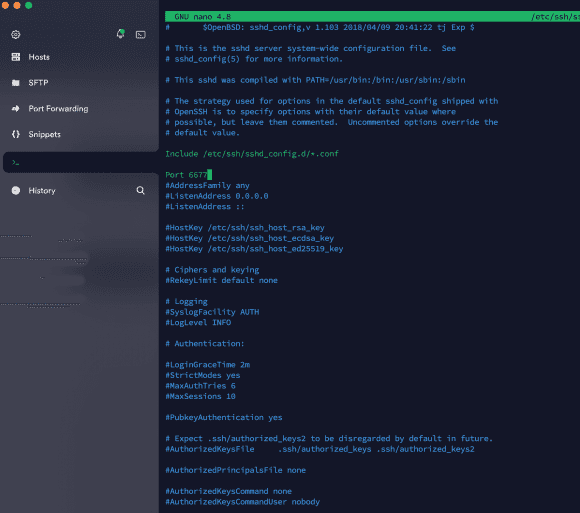
You can scroll down using the down key. Go to where it says #Port 22 and remove the # and enter a custom port between the range 1024 and 65535. For this guide, we chose 6677 as seen in the example below, where the green cursor is.
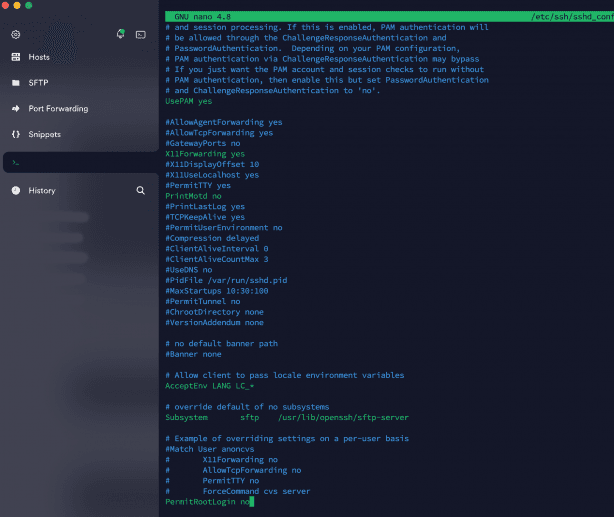
Next, we’re going to disable root login. Scroll down until you find the PermitRootLogin entry. Remove the yes and enter no instead as seen in the screenshot below.
Now, we want to save this setting. To do so, click on Control and x. Then y to confirm and lastly press enter to save. You can further secure the SSH to your liking by checking this guide: 10 steps to properly secure your SSH server. You can optionally also add 2fa protection on the SSH connection for an additional strong security layer. Next, we’re going to restart the SSH protocol. Enter the command below in your terminal.
systemctl restart ssh
Next, we’re going to check the status of the protocol, to check if it was configured properly. Enter the command below in your terminal.
systemctl status ssh
It will output the following, note that it should show your custom port. For this guide, we used 6677
Starting OpenBSD Secure Shell server…
Server listening on 0.0.0.0 port 6677.
Server listening on :: port 6677.
Started OpenBSD Secure Shell server.
Now we’re going to install and configure a firewall to make our system more secure and only allow connections from ports we’ll actually use. Enter the command below in your terminal.
sudo apt install ufw
Now we’re going to deny all incoming connections and later on only allow certain ports. Enter the command below in your terminal.
sudo ufw default deny incoming
Now we’re going to allow outgoing connections. Enter the command below in your terminal.
sudo ufw default allow outgoing
Ports 80 and 443 are not required by MetalGo. Only open them if you intentionally run a separate web service on this server.
# No MetalGo firewall rule is required for ports 80 or 443
Keep the RPC API on port 9650 bound to localhost unless remote access is explicitly required. If you enable remote RPC, allow only a trusted source IP.
sudo ufw allow from YOUR_TRUSTED_IP to any port 9650 proto tcp
Port 9651 is MetalGo’s peer-to-peer staking port and must accept inbound TCP connections for correct node operation.
sudo ufw allow 9651/tcp
Port 1122 is not required by MetalGo. Do not open it unless another service you intentionally run requires it.
# No MetalGo firewall rule is required for port 1122
Grafana port 3000 and Prometheus port 9090 should not be exposed to the public internet. Prefer a VPN or SSH tunnel; otherwise restrict access to a trusted source IP.
# Keep ports 3000 and 9090 private or restricted to trusted IPs
If remote Grafana access is required, replace YOUR_TRUSTED_IP with one trusted public IP. Do not use a broad network range.
sudo ufw allow from YOUR_TRUSTED_IP to any port 3000 proto tcp
Apply the same restriction to Prometheus only if you need direct remote access to it.
sudo ufw allow from YOUR_TRUSTED_IP to any port 9090 proto tcp
Now we’re going to allow connections on our custom port we set up earlier. In this example, it’s port 6677. Enter the command below in your terminal.
sudo ufw allow 6677
Now that we configured all ports, we can enable the firewall. Enter the command below in your terminal.
sudo ufw enable
Now we’re going to check if we configured all ports properly. Enter the command below in your terminal.
sudo ufw status verbose
Verify if the output has all the ports configured correctly, including the custom port we’ve set up. If so, then you’ve successfully set up your machine. Next, we want to exit the session and out. Enter the command below in your terminal.
exit
Now that we’re logged out, we have to verify that we can log in under the newly created username, password, and new port. So make sure to enter your newly created username and custom port in the SSH tool.If we’re able to successfully log in, it’s time to reboot the machine, so the firewall settings take effect. Enter the command below in your terminal.
sudo reboot
You can now continue to Chapter 05: Installing the Metal Blockchain node software.
First, we’re going to update and upgrade all our applications on our operating system to ensure that our system is up to date. Enter the command below in your terminal.
sudo apt-get update && sudo apt-get upgrade -y
Next, we’re going to install htop: an interactive system-monitor process-viewer, and process-manager. Enter the command below in your terminal.
sudo apt install htop
Once completed, we’re going to create a new user. You will be asked to choose a password for this new user. You can optionally enter full name, room number, etc.; to skip, press Enter every time. Enter the command below in your terminal. Note: testnode should be changed with your personally chosen username.
adduser testnode
Next, we’re going to give this new user sudo privileges. Sudo is an acronym for superuser do, a command that runs an elevated prompt without a need to change your identity. Enter the command below in your terminal. Note: testnode should be changed with your personally chosen username.
adduser testnode sudo
Now we’re going to configure the Secure Shell Protocol (SSH), which is a cryptographic network protocol for operating network services securely over an unsecured network. Enter the command below in your terminal.
sudo nano /etc/ssh/sshd_config
You can scroll down using the down key. Go to where it says #Port 22 and remove the # and enter a custom port between the range 1024 and 65535. For this guide, we chose 6677 as seen in the example below, where the green cursor is.
Next, we’re going to disable root login. Scroll down until you find the PermitRootLogin entry. Remove the yes and enter no instead as seen in the screenshot below.
Now, we want to save this setting. To do so, click on Control and x. Then y to confirm and lastly press enter to save. You can further secure the SSH to your liking by checking this guide: 10 steps to properly secure your SSH server. You can optionally also add 2fa protection on the SSH connection for an additional strong security layer. Next, we’re going to restart the SSH protocol. Enter the command below in your terminal.
systemctl restart ssh
Next, we’re going to check the status of the protocol, to check if it was configured properly. Enter the command below in your terminal.
systemctl status ssh
It will output the following, note that it should show your custom port. For this guide, we used 6677
Starting OpenBSD Secure Shell server…
Server listening on 0.0.0.0 port 6677.
Server listening on :: port 6677.
Started OpenBSD Secure Shell server.
Now we’re going to install and configure a firewall to make our system more secure and only allow connections from ports we’ll actually use. Enter the command below in your terminal.
sudo apt install ufw
Now we’re going to deny all incoming connections and later on only allow certain ports. Enter the command below in your terminal.
sudo ufw default deny incoming
Now we’re going to allow outgoing connections. Enter the command below in your terminal.
sudo ufw default allow outgoing
Ports 80 and 443 are not required by MetalGo. Only open them if you intentionally run a separate web service on this server.
# No MetalGo firewall rule is required for ports 80 or 443
Keep the RPC API on port 9650 bound to localhost unless remote access is explicitly required. If you enable remote RPC, allow only a trusted source IP.
sudo ufw allow from YOUR_TRUSTED_IP to any port 9650 proto tcp
Port 9651 is MetalGo’s peer-to-peer staking port and must accept inbound TCP connections for correct node operation.
sudo ufw allow 9651/tcp
Port 1122 is not required by MetalGo. Do not open it unless another service you intentionally run requires it.
# No MetalGo firewall rule is required for port 1122
Grafana port 3000 and Prometheus port 9090 should not be exposed to the public internet. Prefer a VPN or SSH tunnel; otherwise restrict access to a trusted source IP.
# Keep ports 3000 and 9090 private or restricted to trusted IPs
If remote Grafana access is required, replace YOUR_TRUSTED_IP with one trusted public IP. Do not use a broad network range.
sudo ufw allow from YOUR_TRUSTED_IP to any port 3000 proto tcp
Apply the same restriction to Prometheus only if you need direct remote access to it.
sudo ufw allow from YOUR_TRUSTED_IP to any port 9090 proto tcp
Now we’re going to allow connections on our custom port we set up earlier. In this example, it’s port 6677. Enter the command below in your terminal.
sudo ufw allow 6677
Now that we configured all ports, we can enable the firewall. Enter the command below in your terminal.
sudo ufw enable
Now we’re going to check if we configured all ports properly. Enter the command below in your terminal.
sudo ufw status verbose
Verify if the output has all the ports configured correctly, including the custom port we’ve set up. If so, then you’ve successfully set up your machine. Next, we want to exit the session and out. Enter the command below in your terminal.
exit
Now that we’re logged out, we have to verify that we can log in under the newly created username, password, and new port. So make sure to enter your newly created username and custom port in the SSH tool.If we’re able to successfully log in, it’s time to reboot the machine, so the firewall settings take effect. Enter the command below in your terminal.
sudo reboot
You can now continue to Chapter 05: Installing the Metal Blockchain node software.